
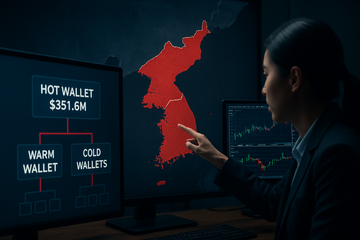
At18:31 UTC on September 24, 2026, Bitget's security systems flagged unauthorized transfers from a limited number of hot wallets. By the time withdrawals were paused and on-chain addresses were blacklisted, attackers had drained roughly $351.6 million across nineteen transactions on five blockchains — making it the largest single centralized-exchange breach of 2026, and the second-largest of the cycle after Bybit's February 2025 $1.5 billion theft.
Funds moved
~$351.6M
Across 19 transfers from hot and warm wallets; cold wallets untouched
Detected
18:31 UTC, Sep 24, 2026
Per Bitget's official security notice, published same day
Largest loss
~157.5M XRP
On-chain tracker Lookonchain; ~31,890 ETH (~85.8M) and ~75.5M stablecoins also moved
Coverage
$464M User Protection Fund
Loss fully covered; ~$112.4M cushion remains after payout
Chain footprint
5 networks
Ethereum, XRP Ledger, Avalanche, BNB Smart Chain, Arbitrum, plus Tron
Attribution
Lazarus Group (suspected)
VPN IP patterns cited by Bitget CEO; no forensic evidence published yet
Attack mechanics
The Breach Bypassed the Keys — It Hit the Backend
CoinDesk and Bitget's own security notice describe the same attack: a third-party software intrusion compromised a critical backend system, spoofed transaction data, and triggered Bitget's authorization process to sign transfers as if they were legitimate withdrawals. CEO Gracy Chen said \"private key compromise has been ruled out\" — meaning the vault doors stayed locked, but the teller behind the counter was tricked.
- Cold wallets remained fully secure; offline keys were never exposed — the breach was contained to the hot and warm tiers of a three-tier wallet architecture.
- Attackers moved funds across Ethereum, XRP Ledger, Avalanche, BNB Smart Chain, Arbitrum, and Tron in19 transactions, complicating cross-chain recovery and freezing.
- Withdrawals were suspended within minutes, deposits stayed open, and Bitget engaged blockchain-intelligence firms (SlowMist, Lookonchain, Arkham) plus law enforcement the same day.
Comparison
Bitget vs Bybit: Same Adversary, Different Vulnerability
The February 2025 Bybit hack — attributed by the FBI to Lazarus's \"TraderTraitor\" cluster — stole $1.5 billion by spoofing a cold-wallet signing interface and redirecting ~500,000 ETH. Bitget's attackers never needed to forge a cold-wallet UI; they compromised the wallet backend directly. The result: the same North Korean adversary just demonstrated two distinct kill chains against two distinct exchange architectures within 20 months, totaling roughly $1.85 billion stolen from two venues alone.
Geopolitical layer
Why the 'Lazarus' Tag Is the Story, Not the Number
Bitget has not yet published forensic evidence supporting the Lazarus attribution — Chen cited VPN IP addresses \"linked to a North Korean hacking group\" and an attack pattern \"resembling earlier operations.\" But the tag itself is what moves the story from technology page to sanctions page. OFAC placed Lazarus Group on the SDN List in April 2022 under North Korea Sanctions Regulations §510.214, and the agency has repeatedly designated downstream wallet addresses and front companies. The same Treasury that polices the Lazarus list is the same Treasury that holds the bills backing Circle's USDC — meaning any US-touching wallet that interacts with Bitget's stolen funds is now operating inside an enforcement perimeter, not just a recovery perimeter.
- DPRK-linked actors stole $2.02B in 2025 (51% YoY) and account for 76% of all crypto hack value through April 2026, per sanctions-tracking research.
- Lazarus is OFAC-sanctioned under §510.214; receiving addresses are routinely added to the SDN list, freezing any USD fiat off-ramp through US banks.
- Bitget announced a Sygnum Protect off-exchange custody partnership the same day as the hack — a structural fix that arrived hours after the loss it was designed to prevent.
US-listed spillover
The Underwriting Question for Coinbase, Circle, Galaxy and Robinhood
Bitget itself is private and Seychelles-domiciled, with no US listing to reprice. But the $351.6M sitting in now-flagged wallets includes roughly $75.5M of USDT and USDC — issued by Tether and Circle Internet Group respectively, the two issuers that anchor the $307B global stablecoin market. Every US-licensed venue that touches a tainted address inherits an OFAC-compliance obligation, and the institutional clients they serve now have a fresh reason to migrate volume onto regulated rails. Coinbase reported a record 10.3% spot-trading-volume market share in Q2 2026 (its third consecutive record quarter) and held an all-time-high $20B of USDC on platform — meaning ~30% of all USDC in circulation already sits inside Coinbase's compliance perimeter.
- Coinbase Q2 2026 revenue: $1.22B, net loss $359M; 10.3% spot volume share (record), stablecoin revenue $292M (Coinbase Q2 8-K, filed Jul 30, 2026).
- Circle Q2 2026 revenue: $701M, net income $48M; USDC market cap ~$78B vs USDT ~$188B; Circle must demonstrate freeze capability on tainted addresses to preserve institutional trust.
- Galaxy Digital operates one of the largest regulated OTC crypto desks and provides institutional custody — the Bitget hack accelerates institutional migration toward qualified custodians like Galaxy, Anchorage, BitGo, Fireblocks.
- Robinhood Q2 2026 revenue: $4.93B TTM, $108.6B market cap; the firm reported 32% YoY revenue growth and a 45x P/E, making any regulatory tailwind from a high-profile offshore breach immediately accretive to retail onboarding.
Stablecoin pathway
USDC and USDT: The Cross-Border Recovery Channel
On-chain trackers identified roughly $75.5 million of stablecoins — split between USDT and USDC — among the stolen assets, with additional movement through Tron and EVM chains. Stablecoins are the cleanest recovery vector because issuers can unilaterally freeze blacklisted addresses at the smart-contract level: Tether's T3 Financial Crime Unit (with Tron and TRM Labs) had frozen over $450M in illicit USDT by May 2026, and USDC's contract includes a blacklist function Circle has used repeatedly. But each freeze requires the issuer to first identify the receiving address — and on a multi-chain, multi-jurisdiction heist, the recovery window closes with every block.
The deeper structural point: the largest two stablecoins ($264B combined) are both pegged to the US dollar and both depend on US Treasury bills for collateral — meaning the US government is the ultimate backstop, the primary regulator, and now the primary sanctions enforcer of the very assets that DPRK is trying to steal. That collision of interests is what converts a $351.6M private loss into a quasi-public policy event.
Regulation
CLARITY Act, Timed One Week Before the Hack
On September 17, 2026 — one week before Bitget's hack — the Senate blocked a procedural vote on the CLARITY Act, the bill that would have divided digital-asset oversight between the CFTC and SEC and given US-registered exchanges a defined federal perimeter. The timing matters: a high-profile offshore breach attributed to a sanctioned state actor, arriving days after Congress fails to deliver a domestic market-structure framework, gives the pro-regulation wing of the crypto lobby the cleanest possible narrative — \"this is what happens when the US doesn't have a clear licensing regime, and customers flee offshore to unsafe venues.\" Expect CLARITY supporters to cite the Bitget attack by name in the next markup.
- Senate CLARITY vote blocked Sep 17, 2026; the bill passed the House earlier in 2026 but lacks a Senate floor vote.
- Bitget, headquartered in Seychelles and operated from Dubai, sits outside any US federal supervisory perimeter — exactly the gap CLARITY was designed to address.
- Re-introduction of the bill is the most direct US policy response to a Bitget-style breach; watch for a Senate Banking Committee markup within 60-90 days.
Horizons
What Moves First — And What Doesn't
Short-term (days to quarters): the immediate price action is in the stablecoin complex and the regulated US venues, not in offshore private exchanges. Circle faces a binary test on its freeze function — if Circle can demonstrate real-time blacklisting of any tainted USDC addresses within the first week, the institutional trust premium widens; if recovery stalls, USDC's relative share of regulated exchange flow erodes. Watch Coinbase's daily spot-volume share for a Q3 print above the Q2 10.3% record.
Long-term (1-3 years): the structural winner is the licensed custody layer — Galaxy Digital, Coinbase Custody, Anchorage, BitGo, Fireblocks — because every institutional dollar that migrates off offshore exchanges lands inside their perimeter. The structural loser is any offshore venue whose underwriting story depends on private-key security theater; Bitget's own move to Sygnum Protect off-exchange custody (announced the same day as the hack) is the template other offshore venues will copy under duress.
Stocks With Verified Linkage to the Bitget Hack
- Record 10.3% spot-trading market share in Q2 2026 (Coinbase Q2 8-K, Jul 30, 2026) compounds as offshore venue risk resurfaces.
- Holds ~30% of all USDC in circulation on-platform; Lazarus attribution turns every tainted USDT/USDC into a regulated-venue tailwind.
- Q3 2026 trading-volume print (due late October) is the next binary catalyst for share-gain confirmation.
- ~$75.5M of USDC and USDT were among Bitget's stolen assets; Circle must demonstrate blacklist-and-freeze capability within days to defend trust premium.
- USDC market cap ~$78B vs USDT ~$188B (Apr 2026); a successful recovery widens the regulated-stablecoin lead, a failure narrows it.
- Q3 earnings early November will reveal whether stablecoin revenue mix shifted toward USDC after the hack.
- Operates one of the largest regulated OTC desks and institutional custody infrastructure — the Bitget hack accelerates migration to qualified custodians like Galaxy.
- Q2 2026 revenue $58.4B TTM includes data-center and digital-asset segments; institutional flow directly accretes to OTC and trading desk revenue.
- Stock at $25.19 vs 52-week high of $45.92 — institutional crypto on-shoring is the catalyst that closes that gap.
- Retail crypto onboarding accelerates when a high-profile offshore hack is in headlines; HOOD reported32% YoY revenue growth in Q2 2026.
- Q2 2026 P/E ~55x leaves room for re-rating if a CLARITY-style regulatory framework follows the Bitget narrative.
- Tokenized-stock perpetuals product positions HOOD to capture volume rotating off offshore derivatives venues like Bitget and Bybit.
- Cash App and Bitkey self-custody wallet create a natural beneficiary if retail users pivot toward self-custody after the hack.
- Block's Q3 earnings (early November) will reveal whether Cash App crypto volumes saw a step-change in the week of Sep 24, 2026.
- Smaller market cap and lower direct crypto-exchange exposure make XYZ a secondary beneficiary vs COIN or HOOD.
- Q2 2026 data-center revenue $33.2M (Riot Q1 release, Apr 30, 2026) is independent of exchange security events but tied to broader crypto sentiment.
- A Bitget-driven Bitcoin sell-off could pressure mining-equity multiples; a regulatory tailwind does the opposite.
- Watch BTC price action in the 72 hours after the hack as the cleanest read on cross-asset sentiment transmission.